How state-sponsored attackers compromised wallet middleware rather than cryptographic keys, drained seven blockchain networks in 18 minutes, and absorbed selling volume through decentralized order aggregators.
Executive Intelligence Brief
- The Core Attack Vector: Bitget confirmed that zero private keys were compromised. The attackers breached an intermediary backend middleware system, forged valid internal withdrawal instructions, and caused the legitimate signing pipeline to authorize transfers.
- Total Capital Extracted: $351.6 million drained across seven networks, led by 102.93 million XRP ($157.5M) and 31,890 ETH ($85.8M), alongside stablecoins and tokenized gold (XAUt).
- Evasion Through Rapid Conversion: The attacker swapped 19.67 million USDT0 into 7,111 ETH within 6 minutes on UniswapX and 1inch Fusion, paying a 5% premium above market spot to absorb liquidity and front-run centralized stablecoin blacklists.
- State Attribution Links: Threat intelligence firms Elliptic and SlowMist traced stolen fund flows directly to addresses associated with the Lazarus Group’s $1.4B Bybit intrusion and the July 2026 AFX Trade compromise.
- Solvency Stress Test: Bitget’s User Protection Fund held approximately $432M to $464M in Bitcoin reserves, leaving a razor-thin surplus after covering the full $351.6M loss.
The Anatomy of a Signing Pipeline Breach
When a centralized cryptocurrency exchange loses hundreds of millions of dollars, the default assumption across retail forums and security incident channels is that someone leaked a mnemonic phrase or compromised a server containing unencrypted private keys.
The security breach sustained by Bitget on September 24, 2026, upends that assumption.
According to official statements from Bitget Chief Executive Officer Gracy Chen, forensic investigations conducted alongside external incident response teams from Mandiant and SlowMist revealed that the exchange’s cryptographic core remained unbreached. The attackers never extracted private keys from cold, warm, or hot wallet infrastructure.
“The attacker compromised the intermediary system that processes and presents orders, not the cryptographic core that authorizes them. They forged transaction data to trigger our own signing mechanisms.”
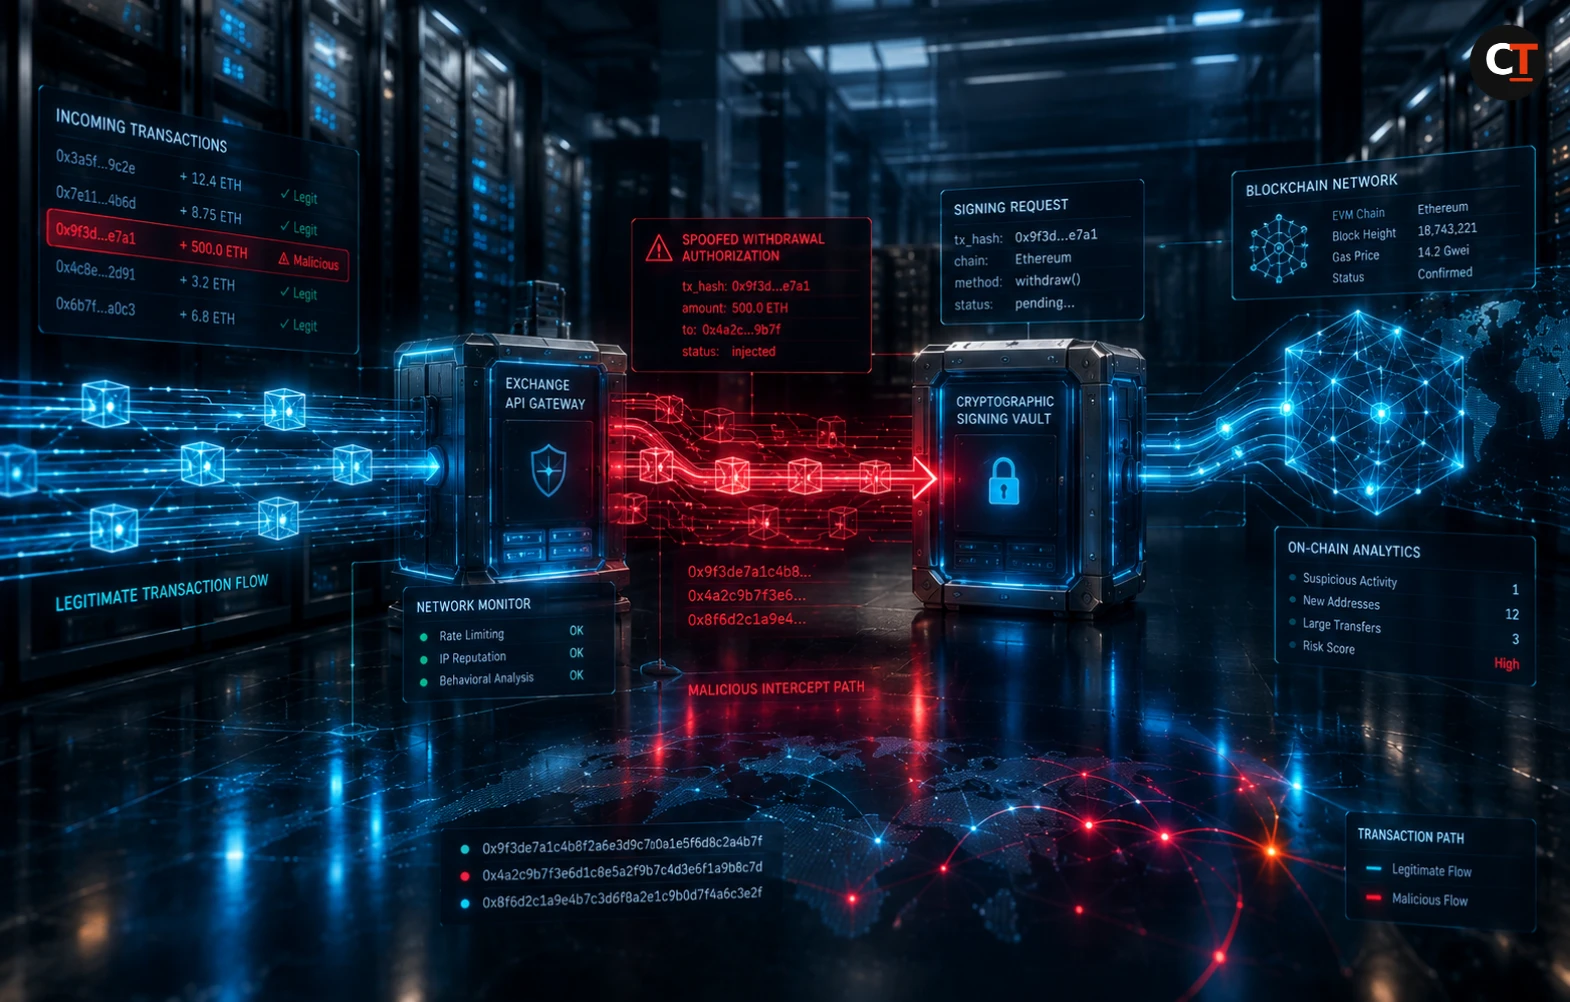
This architectural failure is known in enterprise security as a signing pipeline inversion. Rather than breaking the cryptographic lock, the attackers compromised the administrative logic that controls what the lock signs. In traditional multi-signature or Multi-Party Computation (MPC) environments, signing nodes evaluate incoming transaction requests against pre-configured policy rules: transaction amount thresholds, rate limits, destination address whitelists, and internal database approval states.
By establishing control over an upstream operational service, reported in post-incident briefings as a compromised internal deployment tool, the intrusion group generated valid database state changes. When the automated hot wallet signing service queried the database to verify whether user withdrawal requests were authentic, the poisoned backend responded in the affirmative.
The wallet engine followed its programmed rules. It signed the transactions, broadcast them to public mempools across seven blockchains, and authorized the transfer of customer reserves into attacker-controlled addresses.
The Asset Extraction Matrix: 18 Minutes Across Seven Chains
Between 18:31 UTC and 18:49 UTC on September 24, on-chain forensic monitoring firms at Arkham Intelligence and Lookonchain detected an extraordinary sequence of simultaneous outflows. Five separate hot wallet clusters belonging to Bitget were drained in rapid succession.
The breadth of assets targeted highlights pre-scripted automation. State-sponsored operators do not manually formulate transactions during an intrusion of this scale; they deploy automated drain scripts designed to pull token balances in order of liquidity depth.
| Asset | Quantity Stolen | Realized USD Valuation | Primary Drainage Network |
|---|---|---|---|
| XRP | 102,930,000 | ~$157.5M | XRP Ledger |
| ETH | 31,890 | ~$85.8M | Ethereum Mainnet / Arbitrum |
| USDT | 34,750,000 | ~$34.8M | Ethereum / Tron |
| USDC | 21,050,000 | ~$21.1M | Ethereum / Optimism / Base |
| USDT0 | 19,670,000 | ~$19.7M | BNB Smart Chain |
| XAUt (Tether Gold) | 3,000 | ~$12.8M | Ethereum |
| BNB | 12,719 | ~$9.9M | BNB Smart Chain |
| AVAX | 821,012 | ~$8.4M | Avalanche C-Chain |
| TRX | 20,590,000 | ~$7.1M | Tron Network |
The total tally reached $351.6 million within minutes. Over 44% of the extracted capital was concentrated in XRP, an unusual profile for typical decentralized finance exploits, but entirely consistent with centralized exchange reserve distributions where retail trading volume on alternative layer-one tokens is high.
Verified Primary On-Chain Consolidation Target
EVM proceeds from Ethereum, Arbitrum, Base, Optimism, and BNB Smart Chain were routed through intermediate hops before hitting the attacker’s main consolidation contract:
Etherscan Tagged Address: 0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee (Bitget Exploiter 1)
Bubblemaps forensics confirmed that 15 massive initial transactions moved approximately $192 million across seven assets into this singular node before secondary splitting began.
The Anti-Freeze Maneuver: Aggressive Slippage and Volume Absorption
The greatest operational challenge facing a threat actor who steals centralized stablecoins (USDT and USDC) is the freeze function.
Both Tether and Circle maintain smart contract capabilities to blacklist addresses upon formal requests from law enforcement agencies or emergency disclosures from affected exchanges. If an attacker sits on $55 million in USDT and USDC for more than thirty minutes, there is a high probability that the contract administrator keys will freeze the funds in place, rendering the loot worthless.
To defeat this defensive mechanism, the Bitget attacker executed an aggressive liquidation maneuver that demonstrates how state-sponsored groups view slippage costs.
1. Paying Above Market Spot for Instant Liquidity
Within six minutes of the initial breach, the attacker routed 19.67 million USDT through decentralized order aggregators, primarily UniswapX and 1inch Fusion.
Rather than setting limit orders or staging execution to minimize price impact, the attacker set aggressive slippage tolerances, paying up to 5% above prevailing market rates to fill swaps instantly into native Ether. In total, the group converted stablecoins and alternative assets into 7,111 ETH within minutes, absorbing available automated market maker (AMM) liquidity pools and Private Market Maker (PMM) quotes across the entire Ethereum decentralized ecosystem.
To an institutional algorithmic trader, burning a 5% premium on tens of millions of dollars is catastrophic execution. To a state-backed cyber syndicate operating on a ticking clock against legal freeze orders, paying a $1 million slippage penalty to guarantee an unfreezable asset like native ETH is a routine cost of business.
2. Consolidation into 67,982 Ether
By routing multi-chain tokens across bridge infrastructure including Stargate and Celer’s cBridge, the attacker collapsed fragmented tokens (AVAX, BNB, stablecoins, and tokenized gold) into a unified war chest of 67,982 ETH, valued at approximately $183 million.
Native Ether has no central issuer. There is no contract blacklist function, no administrator key, and no regulatory body that can unilaterally freeze an Ethereum balance at the state level. Once funds are converted into native ETH, the attacker transitions from a sprint against blacklisting to a marathon of obfuscated laundering.
Attribution to Lazarus Group: Infrastructure and On-Chain Fingerprints
During an emergency public briefing on X Spaces, Bitget CEO Gracy Chen confirmed that internal security logs identified IP addresses and virtual private network configurations directly matching historical indicators used by North Korean state-sponsored threat groups.
While IP and VPN data remain confidential pending ongoing investigations with international law enforcement agencies, independent on-chain forensic firms quickly surfaced cryptographic links between the Bitget drainer addresses and known Democratic People’s Republic of Korea (DPRK) operations.
- The Bybit Connection: Threat intelligence analysts at Elliptic and MetaMask’s security lead Taylor Monahan documented that funds originating from the Bitget exploit intersected with wallets previously utilized to launder proceeds from the $1.4 billion Bybit compromise executed earlier in February 2025.
- The AFX Trade Link: On-chain investigator Specter established that portions of the stolen XRP, following cross-chain bridge conversions, flowed into deposit addresses associated with the July 2026 AFX Trade security incident ($24M). That intrusion was formally attributed to UNC4899 (also tracked by federal intelligence as TraderTraitor), an elite cyber-espionage division operating under the Reconnaissance General Bureau of North Korea.
- Software Supply Chain Alignment: The AFX Trade compromise gained initial entry via trojanized developer tooling, poisoned Git hooks, and malicious plugins inside internal build pipelines. Bitget’s preliminary finding that an intermediary operational tool was compromised points directly to the persistent supply-chain tradecraft perfected by Lazarus sub-groups throughout 2024, 2025, and 2026.
The 4-Stage State Laundering Playbook
The liquidation of the Bitget funds matches the four-stage obfuscation methodology documented across major historical heists tracked on CryptechToday’s cybersecurity bit. Understanding this pipeline explains why on-chain freezing efforts struggle once initial consolidation is complete.
- Phase 1: Rapid Cross-Chain Convergence (Hours 0 to 6): Fragmented assets across non-EVM chains (like XRP Ledger and Tron) and secondary layer-two rollups are pushed through non-custodial cross-chain protocols. The goal is to move the capital onto Ethereum mainnet or Bitcoin as fast as possible to access deep liquidity.
- Phase 2: Mixer Splitting and Non-Custodial Pools (Days 1 to 14): Following the partial lifting of US sanctions against Tornado Cash smart contracts in early 2025, usage of the protocol by foreign state actors rebounded sharply. Lazarus routinely breaks 10,000 ETH tranches into hundreds of standardized 100-ETH deposits, cycling through secondary privacy networks and mixers outside Western legal jurisdiction.
- Phase 3: Chain-Hopping and Synthetic Volume Generation: To break deterministic heuristic clustering used by analytics software like Chainalysis and TRM Labs, the group hops capital through THORChain and Chainflip into native Bitcoin. In the 2025 Bybit liquidation, Lazarus converted 86% of stolen Ether into 12,836 BTC across more than 9,100 intermediate transit wallets. During this process, wash trades and decentralized synthetic liquidity pools are used to generate background noise, absorbing large transfers without disturbing global order book spreads.
- Phase 4: Lightly Regulated OTC Desks: The terminal step involves off-ramping into fiat or unbacked stablecoins through over-the-counter liquidity brokers operating in Southeast Asia and Eastern Europe. These entities, such as the regional payment syndicates identified in recent FinCEN enforcement actions, operate with minimal customer identification requirements and facilitate physical cash handoffs or trade settlement for sovereign accounts.
Solvency Assessment: The Bitget Protection Fund Under Pressure
For exchanges operating in the post-FTX environment, the difference between an operational crisis and bankruptcy is the capitalization of their emergency backstops.
Bitget maintains a dedicated User Protection Fund, structurally segregated from ordinary platform operational reserves. According to the exchange’s August 2026 Proof of Reserves report, the fund holds 5,500 BTC, along with supplemental holdings in USDT and USDC.
Because the Protection Fund is heavily denominated in Bitcoin, its nominal valuation fluctuates directly with market pricing. During August 2026, the fund’s value averaged $382 million, closing the month near $432 million as Bitcoin pushed toward $78,500. By the time of the September 24 breach, with Bitcoin trading above $84,000, the protection reserve was valued at approximately $464 million.
Bitget’s leadership has affirmed that all user balances remain fully backed and that the $351.6 million drainage will be absorbed entirely by the Protection Fund. While this confirms immediate platform solvency, the mathematical reality is stark:
- The $351.6M loss consumes approximately 76% of the Protection Fund’s entire balance.
- Covering the loss leaves the reserve with roughly $112 million in residual capital, breaching the exchange’s stated internal policy to maintain the fund above a $300 million permanent floor at all times.
- To restore confidence and maintain institutional tier-one standing, Bitget will need to execute a substantial capital injection to recapitalize the fund back to its baseline reserve ratio.
Strategic Lessons for Institutional Infrastructure
The Bitget breach changes the threat model for institutional digital asset security.
For years, enterprise security posture has fixated almost exclusively on securing private keys: moving from single keys to multi-sig, from multi-sig to MPC, and storing shards inside hardware security modules (HSMs).
The Bitget exploit demonstrates that securing private keys is useless if the authorization system feeding those keys is susceptible to spoofing. If an attacker can inject fraudulent state approvals into backend microservices, the HSM or MPC quorum will faithfully sign illegitimate transfers all day.
Preventing the next nine-figure exchange breach requires engineering teams to treat transaction authorization engines with the same zero-trust isolation applied to private keys:
- Dual-Channel Independent Verification: Hot wallet signing microservices must verify transactions through an out-of-band architecture independent of internal web application databases.
- Algorithmic Velocity Breakers: Automated circuit breakers must be hard-coded into wallet nodes. Draining five separate asset classes across seven distinct blockchains within 18 minutes should trigger automatic cryptographic freezing of hot wallet clusters, regardless of backend database authorizations.
- Rigid Stablecoin Blacklist Monitoring: Exchanges must maintain direct, programmatic integration with stablecoin issuers to coordinate freezes before attackers complete DEX swaps into native Ether.
As North Korean cyber units continue to fund sovereign programs through digital asset extraction, the battleground has shifted. Attackers are no longer looking for keys written on paper or hidden in configuration files. They are targeting the software pipelines that tell the keys what to do.